Prusa patches printer flaws enabling code execution over the network
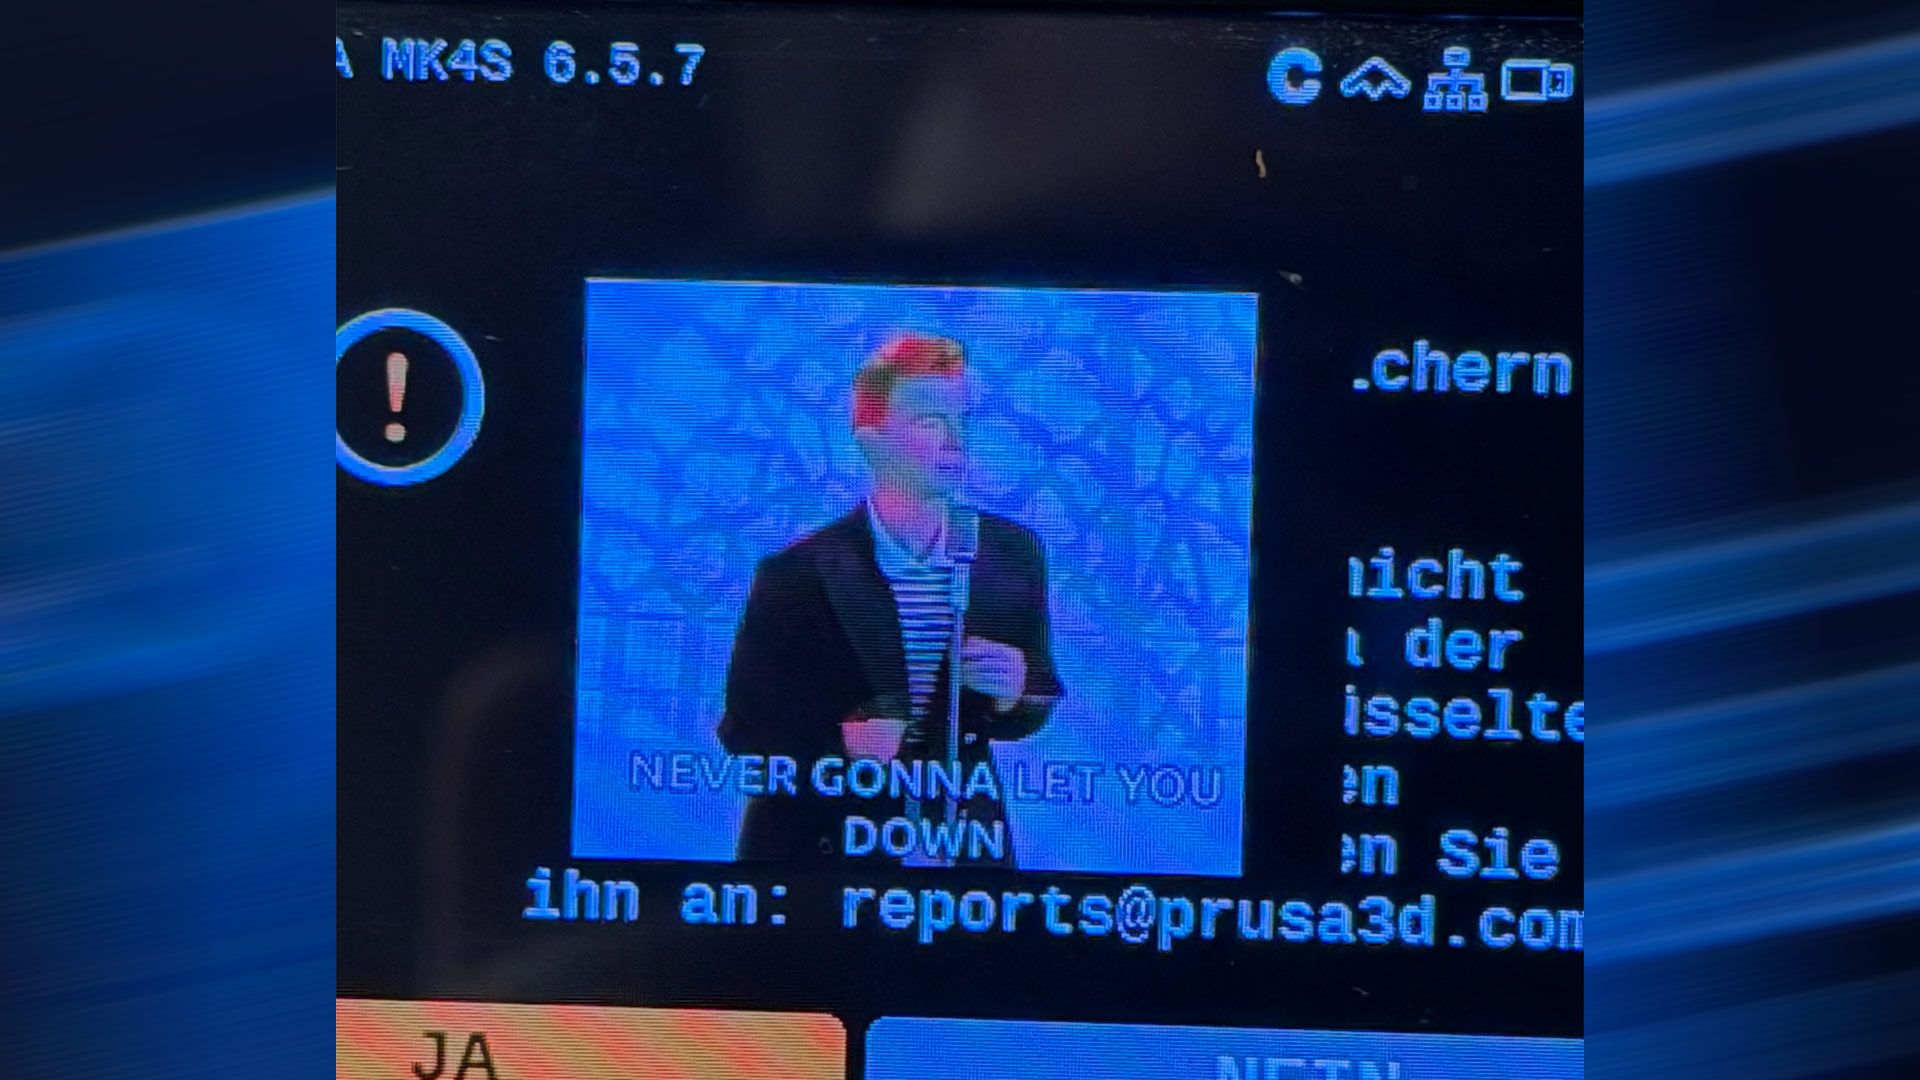 Image: Primary
Prusa has patched vulnerabilities that allowed software engineer Yannick Dixken to run code over the network on his MK4S 3D printer, Tom's Hardware reported. Dixken disclosed 14 findings covering roughly 23 individual defects after a week of testing.
The remote code execution vulnerability carried a severity score of 8.1 and involved Prusa Connect, the cloud or self-hosted management platform. Other findings included attacks using USB filenames, memory overflows triggered by malformed encrypted print files, and network denial-of-service flaws.
Dixken coordinated publication with Prusa. The vulnerabilities are patched in Buddy firmware versions greater than 7.0.0.
Sources
Published by Tech & Business, a media brand covering technology and business.
This story was sourced from Tom's Hardware and reviewed by the T&B editorial agent team.
Back to Newswire