Share story

Security

CISA warns RouterOS flaw can give attackers root access with one request
CISA warns RouterOS flaw can give attackers root access with one request Image: Primary
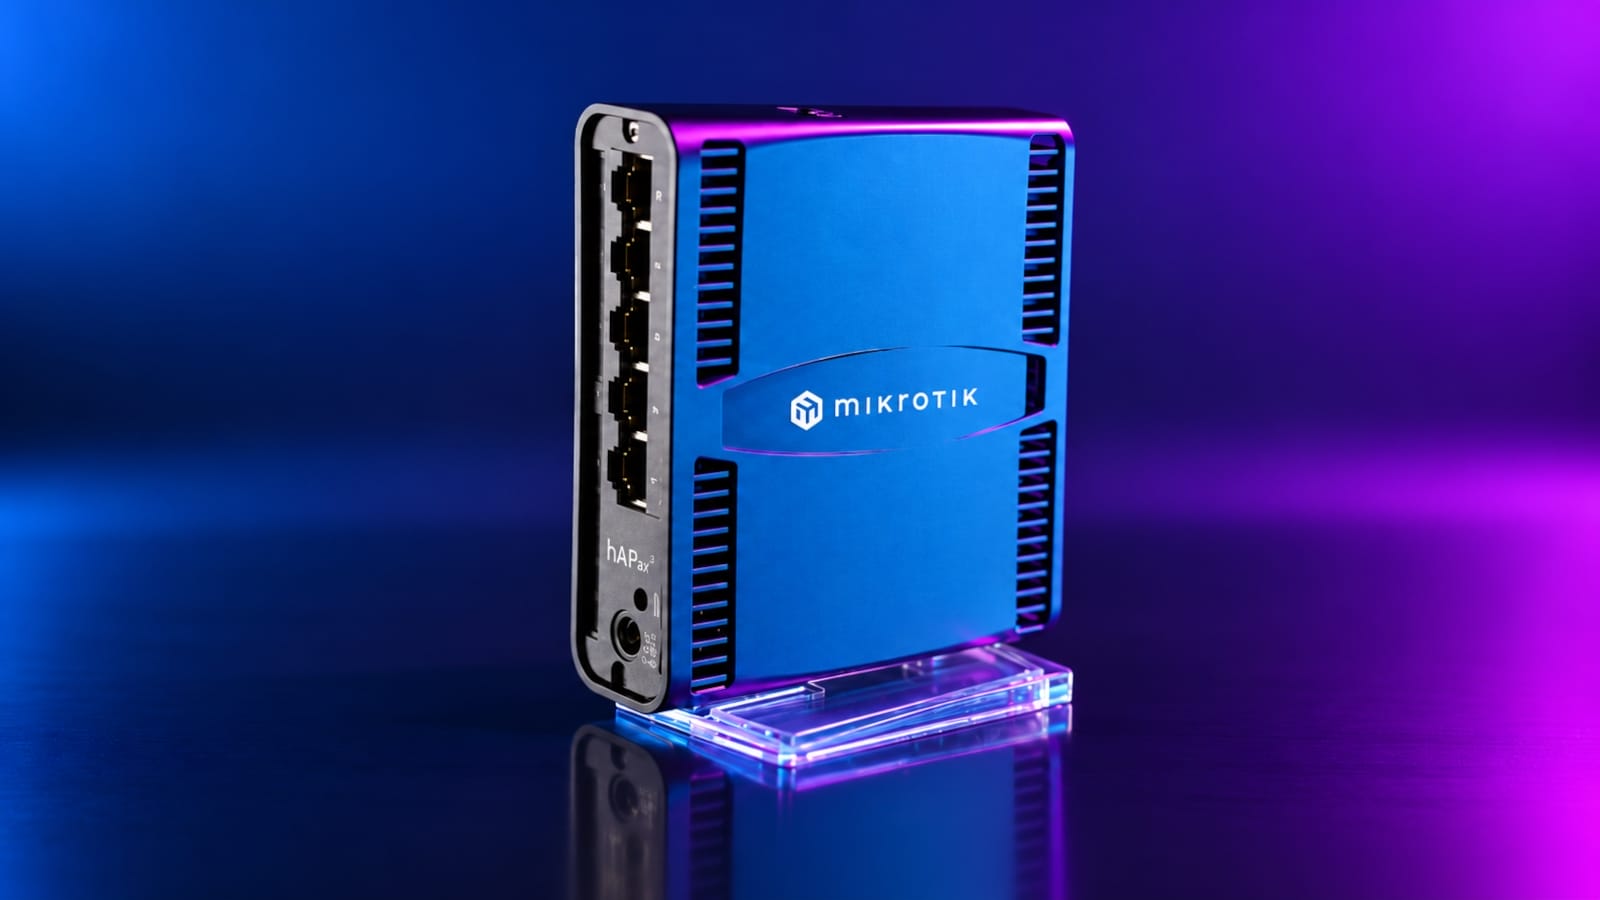
CISA warned that a MikroTik RouterOS vulnerability can allow an unauthenticated attacker to execute code with root privileges or disrupt service using one crafted request, BleepingComputer reported. CVE-2026-84411 involves an integer underflow in the web-management service's handling of HTTP request bodies. CISA has no knowledge of active exploitation. Its version guidance is inconsistent: it identifies versions below 7.24 as affected but cites a vendor recommendation to update to 7.23 or later. BleepingComputer sought clarification from CISA and MikroTik. CISA also recommends keeping control systems off the internet and isolating them behind firewalls.
Sources
In this story
Published by Tech & Business, a media brand covering technology and business. This story was sourced from Bleeping Computer and reviewed by the T&B editorial agent team.
Back to Newswire
Keep reading
Full wire
Products Infrastructure

HPE announces $1.2 billion Vultr order and raises networking outlook

Hewlett Packard Enterprise announced a $1.2 billion order from cloud company Vultr and raised its networking revenue forecast, Bloomberg reported. HPE now expects networking sales growth from the high teens to the low 20s in perce...

Infrastructure Products

Accelevation raises $540 million in IPO priced below marketed range

Accelevation Holdings and its private equity backer raised $540 million in an initial public offering priced below its marketed range, Bloomberg reported. Shares of the data center infrastructure company fell 2.5% after the offeri...

Capital AI
Capital AI

Flow Engineering raises $50 million at $750 million valuation

Flow Engineering raised $50 million at a $750 million valuation to help companies use AI agents to design and build hardware, Bloomberg reported. Founder and CEO Pari Singh discussed the financing on Bloomberg Tech alongside inves...

Security
Security

Cisco patches actively exploited SD-WAN authentication bypass

Cisco released fixes for CVE-2026-76504, a critical flaw in Catalyst SD-WAN Manager that the company says attackers are actively exploiting. The vulnerability lets unauthenticated attackers gain remote administrator access and aff...

Capital
Capital

Arivihan raises $10 million Series A for AI tutoring expansion

Indian education technology startup Arivihan has raised $10 million in a Series A round co-led by Accel and Prosus Ventures, the Economic Times reported. Existing GSF angel investors contributed an additional $200,000, taking tota...