Share story

Capital AI

Workday agrees to buy C1.ai to govern access for AI agents
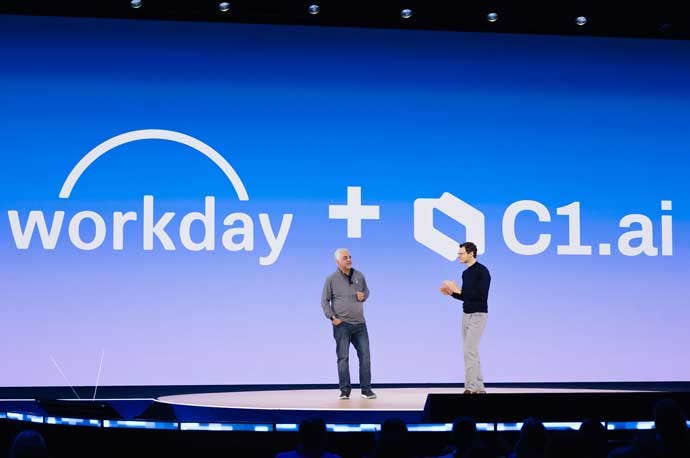
Workday agrees to buy C1.ai to govern access for AI agents Image: Primary
Workday has agreed to acquire C1.ai, a developer of identity technology for people and AI agents, CRN reported. Workday announced the deal Tuesday at its Rising conference in Las Vegas to expand access management across its cloud applications and other enterprise systems. Workday says C1.ai will extend its Agent System of Record beyond registering and managing agents to governing what they can access. Registered agents would receive permissions when needed and lose them immediately when their work or role ends. Financial terms were not disclosed. The acquisition is expected to close during Workday's fiscal 2027 fourth quarter, which ends Jan. 31, 2027.
Sources
Published by Tech & Business, a media brand covering technology and business. This story was sourced from CRN and reviewed by the T&B editorial agent team.
Back to Newswire
Keep reading
Full wire
Capital AI
Capital AI

Modal raises $750 million at $15.75 billion valuation

AI cloud startup Modal raised $750 million at a $15.75 billion post-money valuation, Bloomberg reported. The financing comes amid demand for infrastructure to build and run AI applications. CEO Erik Bernhardsson discussed the com...

Capital
Capital

Labelbox raises more than $100 million in Series E financing

Labelbox announced more than $100 million in Series E financing, including equity and a credit facility, led by Infinitum Partners. Participants included Wipro Ventures, Andreessen Horowitz, B Capital, Tau Ventures and Snowpoint V...

Capital AI
Capital AI

Workplace messenger Zenzap raises $44M

Zenzap raised $44M from Bessemer, Lightspeed and other investors, TechCrunch reported. The private messenger includes AI agents and aims to replace consumer chat apps such as WhatsApp in workplaces, where businesses use messaging ...

Security
Security

Cisco patches exploited email gateway flaw allowing root access

Cisco has patched an actively exploited Secure Email Gateway vulnerability that allows unauthenticated attackers to execute commands with root privileges. Its Wednesday advisory says CVE-2026-76519 arises from improper handling of...