Share story

Security

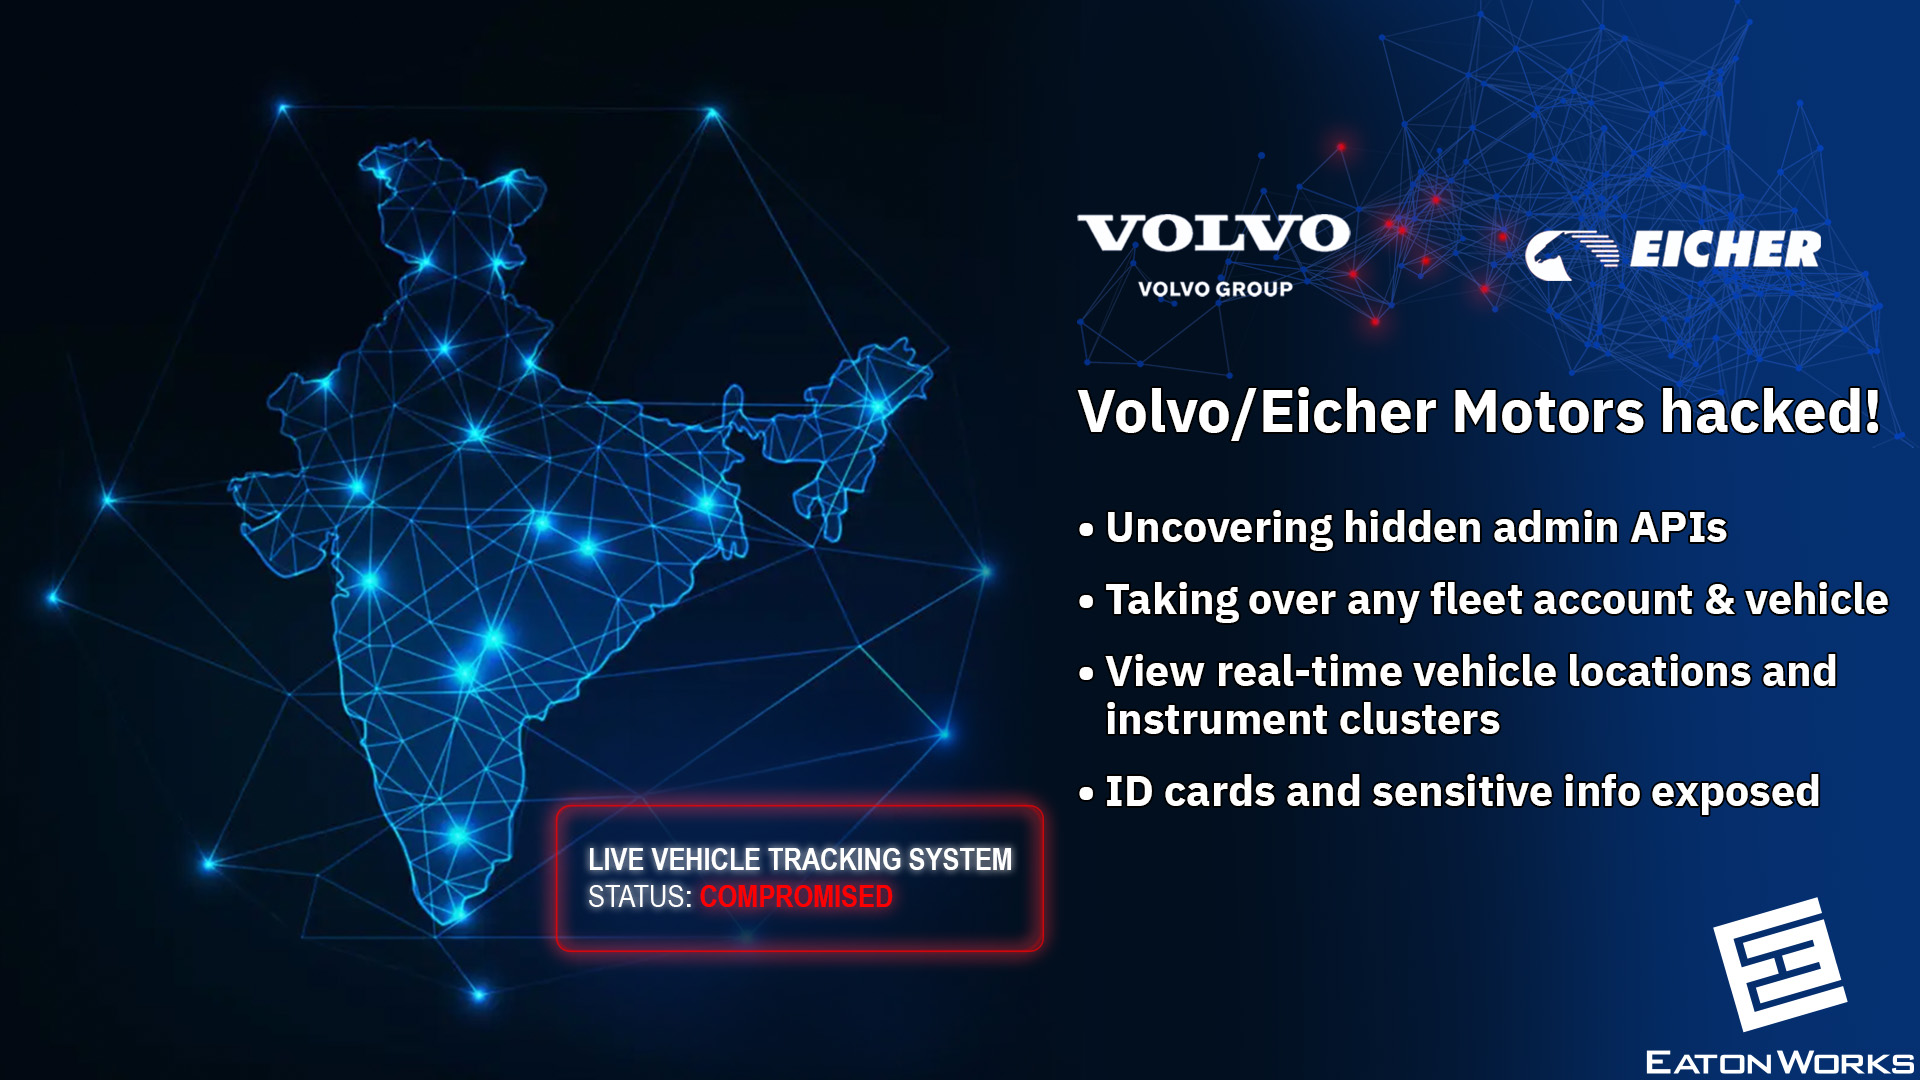
Exploiting Volvo/Eicher's fleet platform to gain control over all users/vehicles
Promo/Hero Graphic Image: Primary
Exploiting Volvo/Eicher's fleet management platform to gain control over all users and vehicles. The vulnerability was discovered in the APIs of My Eicher, a fleet management system built by VE Commercial Vehicles, a joint venture between the Volvo Group and Eicher Motors. The flaw allowed access to unauthenticated internal/admin APIs, enabling account takeover and control over fleets of hundreds of vehicles. As of November 2024, 275k vehicles and 115k customers were registered, though later data showed 676k vehicles and 748k customers. The vulnerability was reported to VECV in November 2025 and fixed by November 20, 2025, before being publicly disclosed on July 27, 2026.
Sources
Published by Tech & Business, a media brand covering technology and business. This story was sourced from eaton-works.com and reviewed by the T&B editorial agent team.
Back to Newswire
Keep reading
Full wire
AI Science
AI Science

ALTO recipe narrows four-bit model training gap in simulated tests

Researchers report in a preprint that ALTO, an open-source training recipe for the 20-billion-parameter GPT-OSS-20B model, reduced the extra training steps needed with four-bit arithmetic. On the MLPerf Small MoE Training benchmar...

Security
Security

Unit 42 reports PHP2Shell breach at European government entity

Attackers exploiting PHP2Shell vulnerabilities accessed password hashes and multi-factor authentication secrets at a European government entity within two hours of initial exploitation, Palo Alto Networks Unit 42 said. They also e...

Security
Security

Python security releases block compromised eMudhra certificate keys

Python's release team issued expedited security updates for five version branches to block compromised eMudhra intermediate certificate authority keys. The team says the change protects normal uses of pip, including upgrading pip ...