Share story

Security

Report URI says 15,579 websites remain infected with malicious JavaScript
Report URI says 15,579 websites remain infected with malicious JavaScript Image: Primary
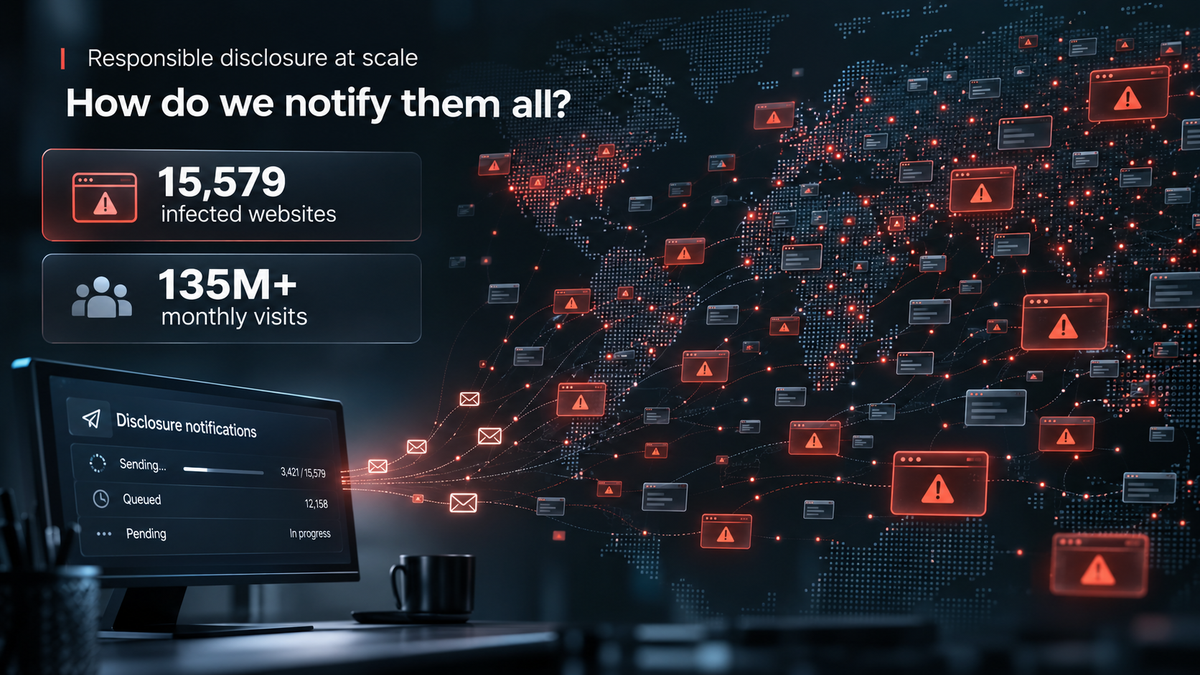
Report URI has identified 15,579 websites that remain infected with malicious JavaScript, Scott Helme wrote, estimating that the sites receive more than 135 million visits each month. The attacks include payment card skimming, malware installation tricks, device exploitation and malicious redirects. The company finds infections through direct website compromises, infected third-party scripts, injected code and expired domains that websites still use to load scripts. Helme said detection now outpaces Report URI's ability to notify affected organizations: contact information is scarce and most messages go unanswered. The company is offering regional lists to national cybersecurity centers and computer emergency response teams to help reach site operators.
Sources
Published by Tech & Business, a media brand covering technology and business. This story was sourced from scotthelme.co.uk and reviewed by the T&B editorial agent team.
Back to Newswire
Keep reading
Full wire
Products
Products

Fox closes $22 billion Roku acquisition

Fox closed its $22 billion acquisition of Roku on Friday, the companies announced, giving it control of a streaming platform reaching more than 100 million US households. Roku founder Anthony Wood now serves on Fox's board.

Capital
Capital

Aave Labs acquires Avon team and lending technology

Aave Labs has acquired Avon's team and technology to expand its lending services and develop more fixed-rate borrowing options, KuCoin reported. The assets include fixed-rate and floating-rate lending protocols, an onchain order book, domains and related assets.

Security
Security

Veeam distributes fixes for critical Linux kernel vulnerability

Veeam said on Friday that some of its products are affected by CVE-2026-98432, a critical Linux kernel vulnerability, BleepingComputer reported. The flaw allows remote unauthenticated attackers to execute commands as root on servers running Multipath TCP listeners.