Security

CISA orders federal agencies to patch exploited Pixel modem zero-day in three days
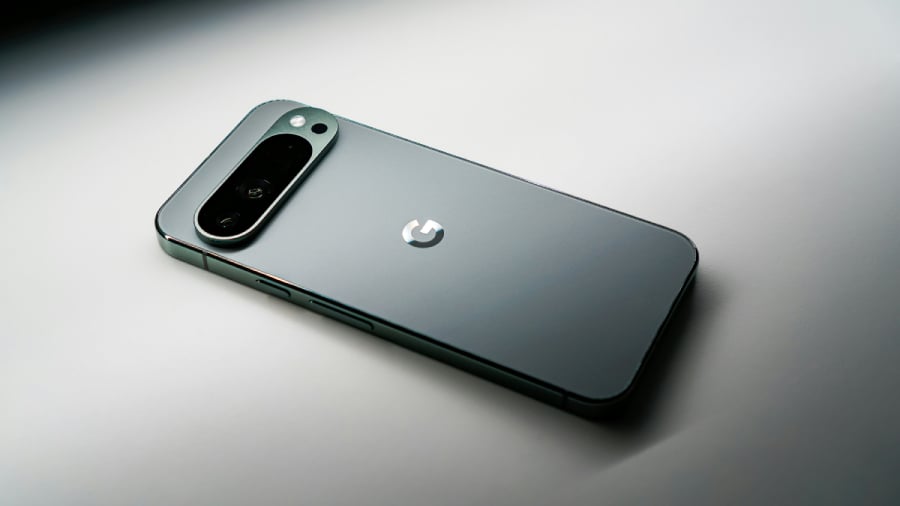
CISA orders federal agencies to patch exploited Pixel modem zero-day in three days Image: Primary
Google disclosed that attackers actively exploited CVE-2026-58704, a high-severity flaw in the cellular modem of Pixel smartphones, before a fix was available. The defect allows an adjacent attacker to escalate privileges without any user interaction, such as clicking a link or answering a call. Google said in its September Pixel security bulletin that there are indications the flaw may have been under limited, targeted exploitation. CISA added the vulnerability to its Known Exploited Vulnerabilities catalog and directed affected federal agencies to remediate within three days. Google patched the flaw in its September 2026 Pixel security release alongside more than 100 other device-specific fixes.
Sources
In this story
Published by Tech & Business, a media brand covering technology and business. This story was sourced from TechRepublic and reviewed by the T&B editorial agent team.
Back to Newswire
Keep reading
Full wire
AI
AI

Moonshot AI's Kimi K3 now available on Amazon Bedrock

AWS has made Kimi K3 from Moonshot AI available on Amazon Bedrock, describing it as the first open-weight model to reach 2.8 trillion parameters. The model combines native vision capabilities with a 1-million-token context window...

AI Infrastructure
AI Infrastructure

AWS launches GPU-aware SageMaker HyperPod Inference Gateway

AWS announced general availability of the SageMaker HyperPod Inference Gateway, a Kubernetes-native routing addon that places inference requests using real-time GPU signals such as KV cache utilization, queue depth, LoRA adapter r...

Security
Security

Cisco patches max-severity ISE zero-day under active exploitation

Cisco released security updates for a maximum-severity authentication bypass in Identity Services Engine and ISE Passive Identity Connector, tracked as CVE-2026-76460, and said its Product Security Incident Response Team is aware ...

Security
Security

Cisco warns of actively exploited ISE authentication bypass

Cisco warned that CVE-2026-76460, a maximum-severity flaw in Identity Services Engine and ISE Passive Identity Connector, is being actively exploited. The reported API authentication-control weakness can let an unauthenticated rem...