Share story

Security

Elastic documents REVSTEALER-linked modules that disable Windows defenses

Elastic documents REVSTEALER-linked modules that disable Windows defenses Image: Primary
Elastic Security Labs documented four previously unreported programs associated with the REVSTEALER Windows information stealer. One module, LockAppHost, can add Microsoft Defender exclusions, disable Windows Update services and tasks, and hide a cryptocurrency miner in legitimate Windows processes. Elastic said the modules persist after the core stealer deletes itself. The connection is based on shared code and investigative context: Elastic did not observe the modules being delivered to a live REVSTEALER host. The stealer has been distributed through game-cheat lures and impersonated or pirated software, including a fake Claude application.
Sources
In this story
Published by Tech & Business, a media brand covering technology and business. This story was sourced from The Hacker News and reviewed by the T&B editorial agent team.
Back to Newswire
Keep reading
Full wire
AI Security
AI Security

GitLab opens beta dashboard for auditing coding agents

GitLab introduced a beta AI Governance Dashboard for Premium and Ultimate customers that brings its own coding agents and connected external agents into one audit view. It links agent activity to developers and projects, showing s...

Security
Security

Go security releases block eight certificate authority keys

Go 1.27.3 and Go 1.26.10, released October 20, reject certificate chains passing through eight intermediate certificate authority keys, The Hacker News reports. The Go team recommends immediate upgrades, citing security concerns a...

Security
Security

Hacker sentenced to eight years over tax-business phishing scheme

Chukwuemeka Victor Amachukwu was sentenced to eight years in prison for his role in spearphishing attacks against U.S. tax preparation businesses, authorities announced Monday. He pleaded guilty to conspiracy to commit computer in...

Policy AI
Policy AI

US orders civilian agencies to remove DeepSeek technology

The United States has ordered federal civilian agencies to stop buying DeepSeek products and services and remove them from government IT systems, according to the Department of Homeland Security. The restrictions also cover third-...

Security
Security

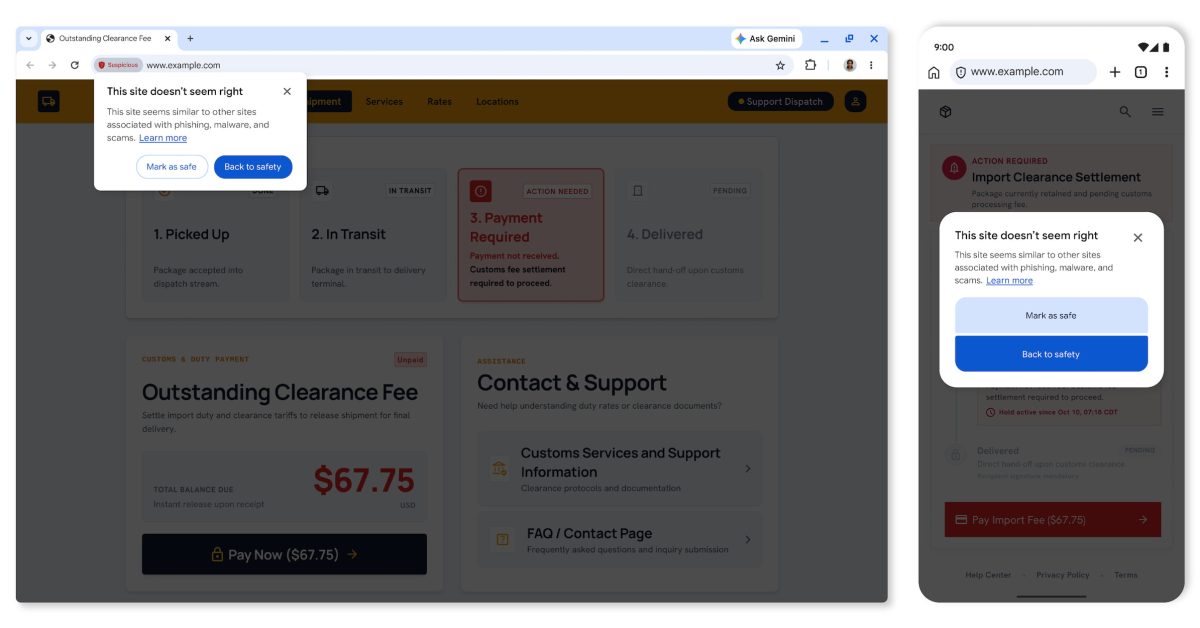
Chrome adds warnings for suspicious sites and copied scam commands

Google announced new Chrome Enhanced Protection defenses that check suspicious websites and warn about copied commands used in ClickFix scams, 9to5Google reported. Those scams persuade users to run commands that install malware, b...