Share story

Products Infrastructure

Stripe opens public preview of real-time Postgres data sync
Stripe opens public preview of real-time Postgres data sync Image: Primary
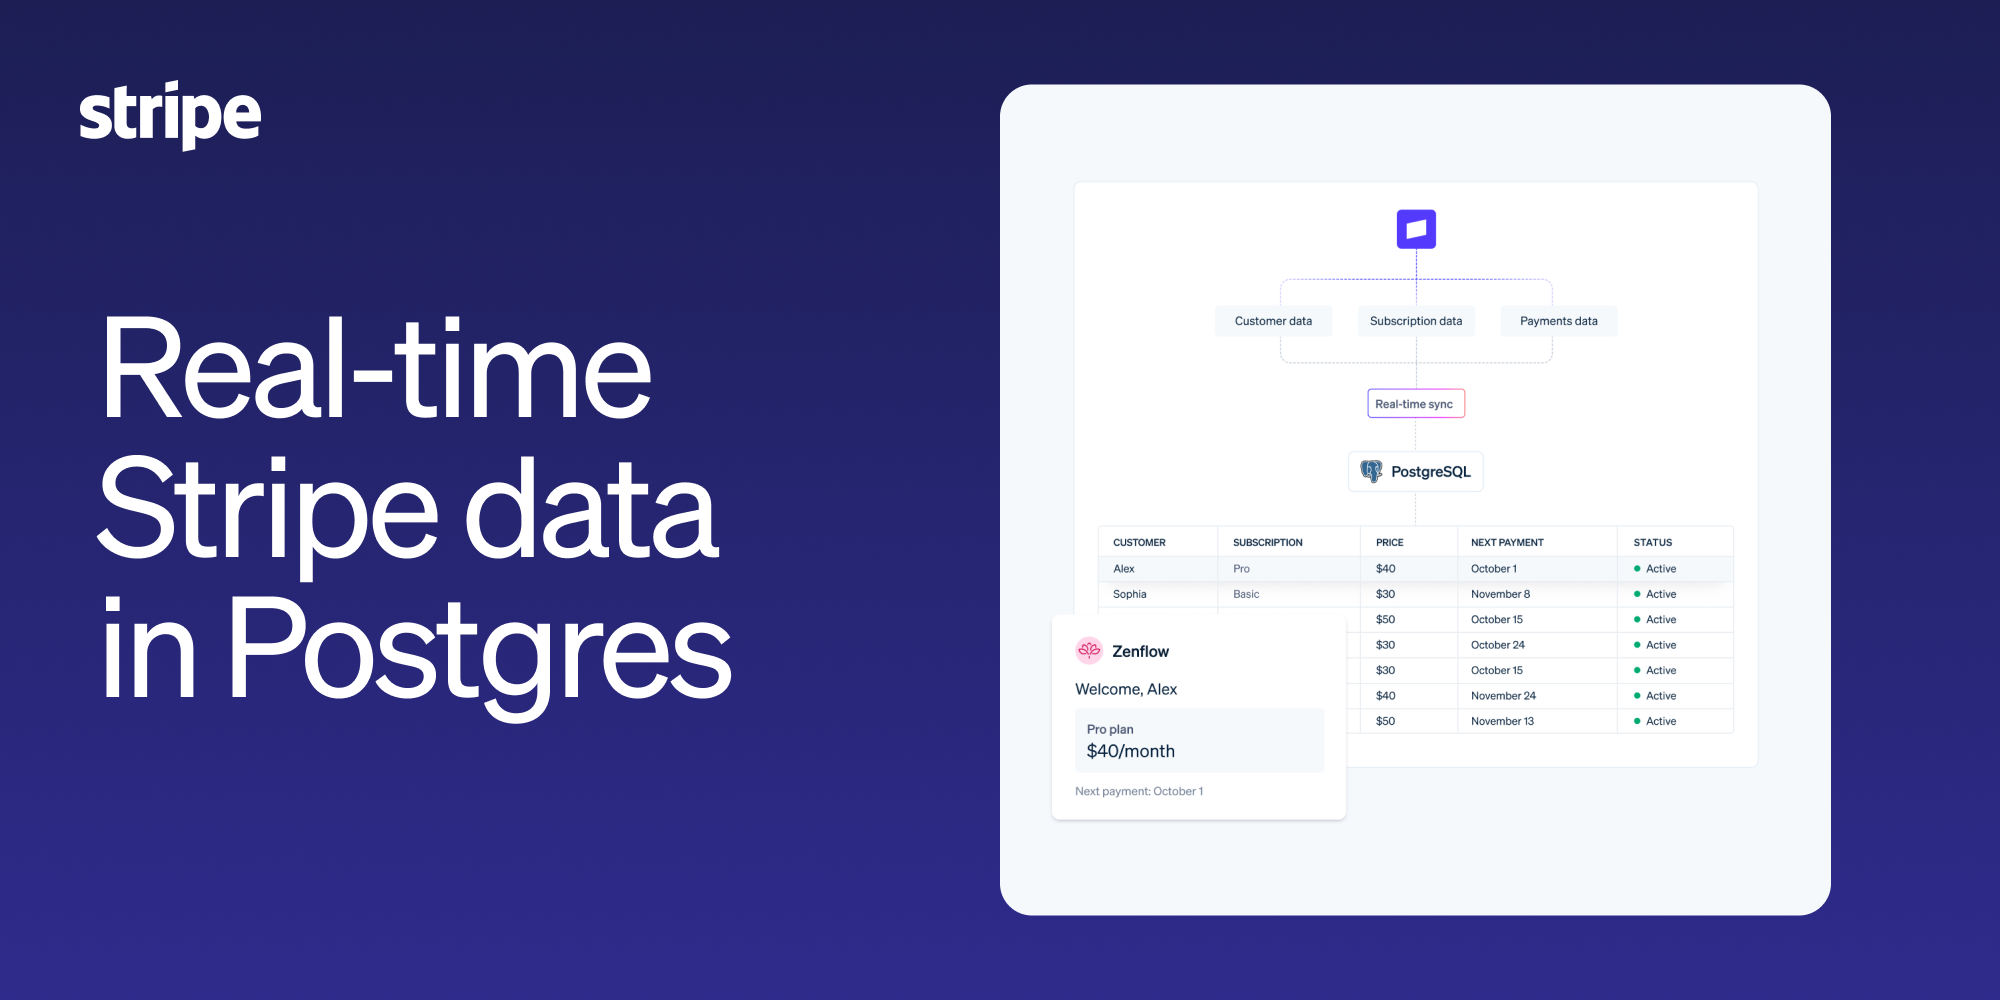
Stripe launched a public preview that synchronizes payment, customer, subscription and other Stripe data directly to Postgres databases through Data Pipeline. The company says updates arrive in seconds, allowing applications to use current Stripe records without developers building their own API polling or webhook infrastructure. Developers connect a database and select tables; Data Pipeline copies existing records, delivers changes and audits synchronized data against Stripe to resolve discrepancies. Supported destinations include Postgres databases hosted by Supabase, AWS, Neon and Databricks Lakebase. The preview is free to get started. Postgres is the first destination with real-time sync; support for other warehouses and storage platforms is coming later.
Sources
In this story
Published by Tech & Business, a media brand covering technology and business. This story was sourced from Stripe Blog and reviewed by the T&B editorial agent team.
Back to Newswire
Keep reading
Full wire
Capital Products
Capital Products

Ramp raises $1.85 billion at $60 billion valuation

Ramp said it raised $1.85 billion at a $60 billion valuation, four months after raising $750 million at a $44 billion valuation. Dragoneer Investment Group, Thrive Capital, Founders Fund, Sands Capital and Avenir Growth co-led the...

Capital
Capital

Spill Games raises $10.5 million to expand mobile games business

Indian mobile games studio Spill Games has raised $10.5 million in Series A funding led by Elevation Capital, with participation from existing investors Centre Court Capital and PeerCapital. The Bengaluru company plans to expand i...

Security AI
Security AI

Langflow flaw draws 1,423 exploit attempts against honeypots

Attackers have made 1,423 exploitation attempts against Previdian's honeypots targeting a critical Langflow vulnerability, The Hacker News reported. The flaw, CVE-2026-105740, affects versions before 1.9.0 and lets authenticated u...